How DevOps Managed Services Simplify Delivery with Azure?
DevOps managed services help organizations streamline software delivery by automating and managing CI/CD workflows, reducing deployment risk, and improving quality — especially...
Integrate security into all phases of development with our Azure DevSecOps
Services to release faster, stay compliant, monitor continuously, and create resilient cloud-native apps.
 Azure DevSecOps Services Ensure Security
 24/7 Support and Maintenance
 Optimize Costs with Smart Solutions
 Enhanced Collaboration and Risk Management
Fill Out the Form and Our Experts Will Contact You Within 24 Hrs


Integrate security, compliance, and monitoring directly into your DevOps workflows.
Book a DevSecOps Consultation
It can be a bit tricky when you decide to move from DevOps to Azure DevSecOps services, but you can still achieve it with proper planning.

Our agile Azure DevSecOps services team provides threat modeling and conducts various risk assessments, which helps them analyze the threats and responsiveness of their assets. In addition to it, they can acknowledge the security controls and pay more attention to those who need more modifications.

You can consider a DevSecOps cyber security strategy successful only if the security, development, and operations teams work in coordination while embedding security controls and processes into the complete DevOps workflows. Continuously monitoring the development process for security concerns and providing quick responses are essential for integrating security operations.

When you integrate security measures with the development process, it involves examining the development workflows while making sure you get minimum disruptions with automation and security practices.

You must match your security procedures with legal and regulatory requirements when using a DevSecOps methodology. By implementing automated compliance checks, audit trials, and policy enforcement tools, you may uphold security standards while simultaneously guaranteeing conformity to industry requirements.
Leverage Bloom’s experienced DevSecOps consultants to increase the security of your software. We provide strong protection, efficiency, and compliance by smoothly integrating security into your development lifecycle.
 Dynamic Expertise
We help businesses implement robust security measures with our in-depth knowledge, so they get the most secure outputs. We guarantee security against potential security threats on your systems and apps.
 Holistic Approach
We emphasize implementing DevSecOps methodologies right from the initial phase as we believe that security is one of the most essential elements during the development phase and must not be considered an afterthought.
 Track of Accomplishments
With over a decade of experience, we have helped numerous organizations from different industries achieve their business goals with our Azure DevSecOps services. From healthcare providers to financial institutions, we have helped businesses thrive in the competitive market.
 Proactive Threat Detection
Reinforced with advanced technologies and tools, our DevSecOps consultants provide unmatched threat detection. We consistently analyze and monitor your systems for any signs of suspicious activities or intrusion. Therefore, ensuring the safety and integrity of your data.







Microsoft Azure offers a suite of integrated tools that enhance DevSecOps practices by embedding security, compliance, and automation across development, deployment, and operations. As a trusted DevSecOps consulting company, Bloom helps organizations leverage these tools to build secure, efficient, and well-governed software delivery pipelines.
Azure Repos provides secure Git-based repositories for version control. It enforces branch policies and code reviews to prevent unverified or risky code merges, forming a core element of Bloom’s DevSecOps consulting services that focus on secure coding practices and version control governance.
Azure Pipelines enables Continuous Integration (CI) and Continuous Deployment (CD), integrating automated testing tools such as SAST, DAST, and secret scanning within workflows. Our expert DevSecOps consultants design and optimize these pipelines to maintain security, speed, and compliance throughout the development lifecycle.
This solution provides Cloud Security Posture Management (CSPM) and Cloud Workload Protection (CWPP), offering visibility into security posture across pre-production and runtime environments. It also scans container images to detect vulnerabilities before deployment.
Azure Key Vault protects sensitive credentials like API keys, passwords, and certificates by securely managing them, eliminating the need to embed secrets in source code.
Microsoft Entra ID manages identities and access controls through features such as Multi-Factor Authentication (MFA), Role-Based Access Control (RBAC), and identity protection to ensure secure access to Azure resources.
Azure Policy enforces compliance and governance by applying configuration rules automatically across resources. This proactive approach is a key part of Bloom’s DevSecOps managed services, ensuring consistent security and policy adherence in cloud environments.
Embrace the benefits of Azure DevSecOps services by integrating security into the core of the software development lifecycle. Reduce vulnerabilities in production code and mitigate the risk of costly breaches.

DevSecOps consulting services empower businesses to deliver quality codes seamlessly and reduce the risk of vulnerabilities. This leads to faster time-to-market and provides a competitive edge in responding to market demands quickly.

DevSecOps managed services is a continuous phase even after the end of the development process. Thus, resulting in better quality software that fulfills customer expectations and encourages more engagement.

Overcoming organizational silos is one of the key pillars of the DevSecOps model. You can further develop an environment where knowledge transfer and collective problem-solving are prominent.

Organizations may produce secure, high-quality apps with fewer vulnerabilities by making security a top priority throughout the development process. This proactive strategy reduces service interruptions, improves user experience, and increases customer trust.

DevSecOps services and solutions offer security from back to front. You can actively identify and resolve vulnerabilities as and when they arise with security controls, automated security testing, and continuous monitoring.

DevSecOps services allow you to save your hard-earned money by optimizing automated monitoring and testing. Allow swift response and identification of potential threats. Thus, reducing the financial impacts and consequences of security breaches.
We help organizations strengthen cloud security by integrating DevSecOps practices into Azure deployment workflows.

The client was releasing software manually, which caused delays, errors, and slowed down innovation. Their small team needed a faster and more reliable way to deliver new features without increasing risk.
We automated their software release process using Azure DevOps. Confirmed updates could now be deployed quickly and safely, with fewer issues. This helped the team launch features faster, reduce errors, and focus more on building great products instead of managing deployments.
Read Case Study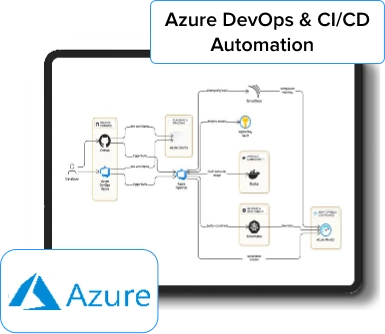
The client faced frequent issues during software updates, which caused delays and downtime in systems used by supply chain teams, retail partners, and customer-facing platforms. Manual processes made it hard to release updates quickly in a fast-moving market.
We automated and standardized their software release process using Azure DevOps. This reduced errors, sped up deployments, and made it easier for teams to launch new digital initiatives faster, helping the business stay competitive and respond quickly to market demands.
Read Case Study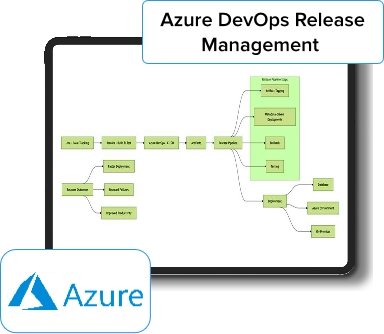
Different teams were using separate tools and manual processes to release software, which caused delays, errors, and poor coordination across plants. The client needed a simpler and more consistent way to manage software updates.
We brought all their tools and processes into a single Azure DevOps setup. By automating releases and improving visibility, teams could deliver updates faster, with fewer issues, and work together more effectively across the organization.
Read Case Study






In simple terms, DevSecOps stands for development, security, and operations. It can be defined as the process of integrating security into all the phases of software development.
DevOps emphasizes streamlining software delivery with automation and collaboration by its side between development and operations teams. DevSecOps, on the other hand, further supports it by integrating security practices into every stage in the development lifecycle.
DevSecOps offers various benefits, such as improved software quality, faster time-to-market, enhanced collaboration, better customer satisfaction, and increased efficiency. If you are looking for Azure DevSecOps services, you can contact us today!
DevSecOps can be concluded as the practice of embedding security testing at every stage of the software development process. It further includes processes and tools to foster collaboration between operations, security, and development teams to develop secure and efficient software.
We provide complete Azure DevSecOps services that integrate continuous exploration, integration, deployment, testing, monitoring, and release automation for products of all sizes. Our approach ensures security, automation, and scalability by using CICD pipelines, security testing, real-time monitoring, and compliance-driven release automation. We minimize risks, increase productivity, and optimize development for safe, efficient software delivery.
We Integrate Security Into Every DevOps Stage.